 1 / 11
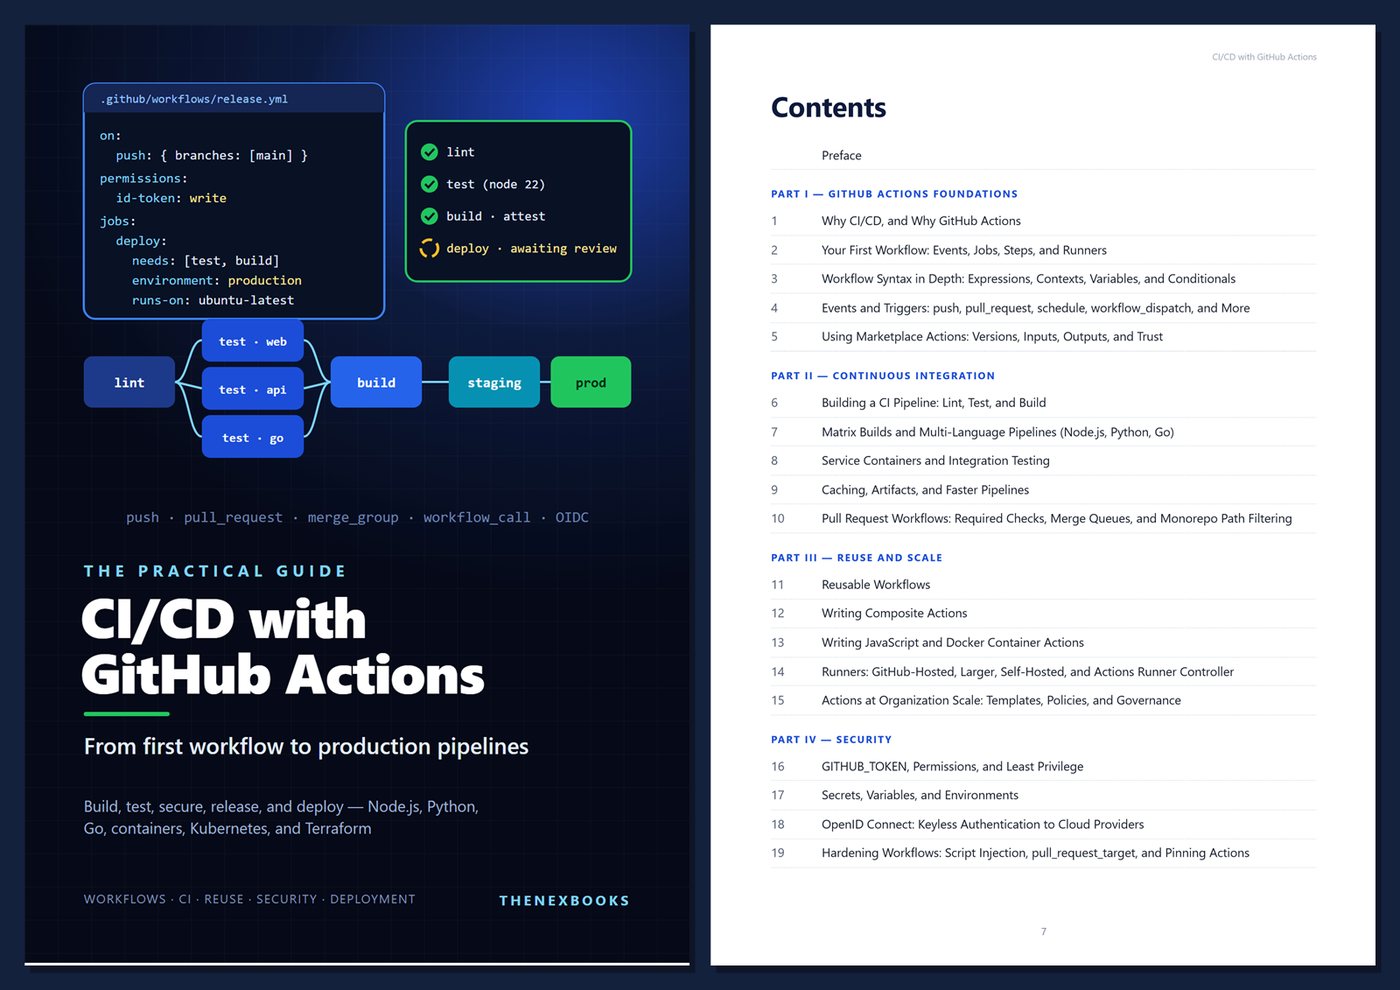
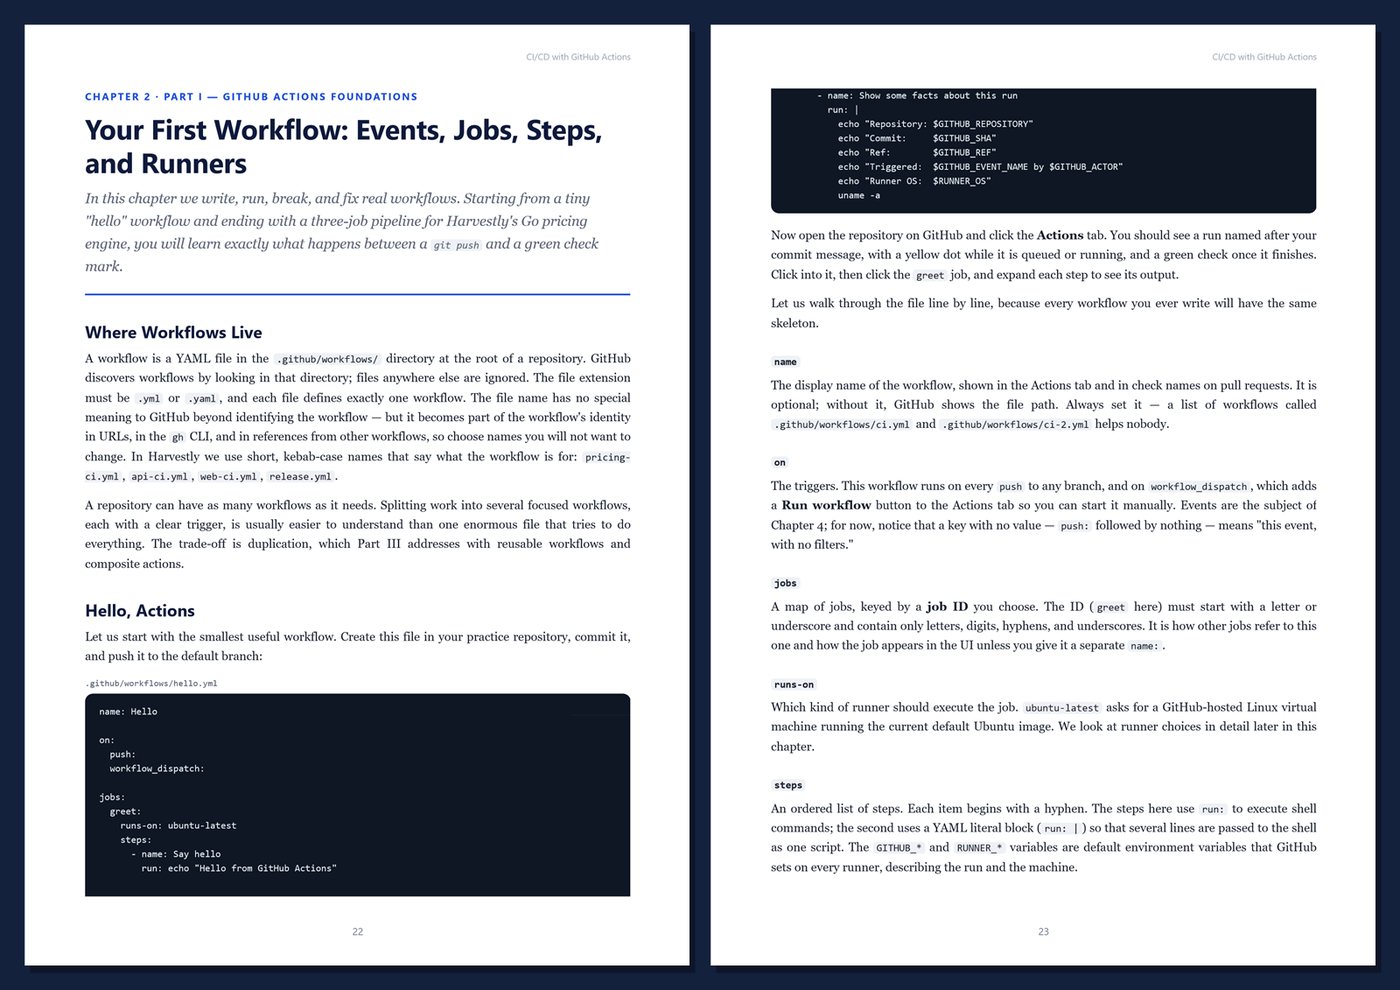
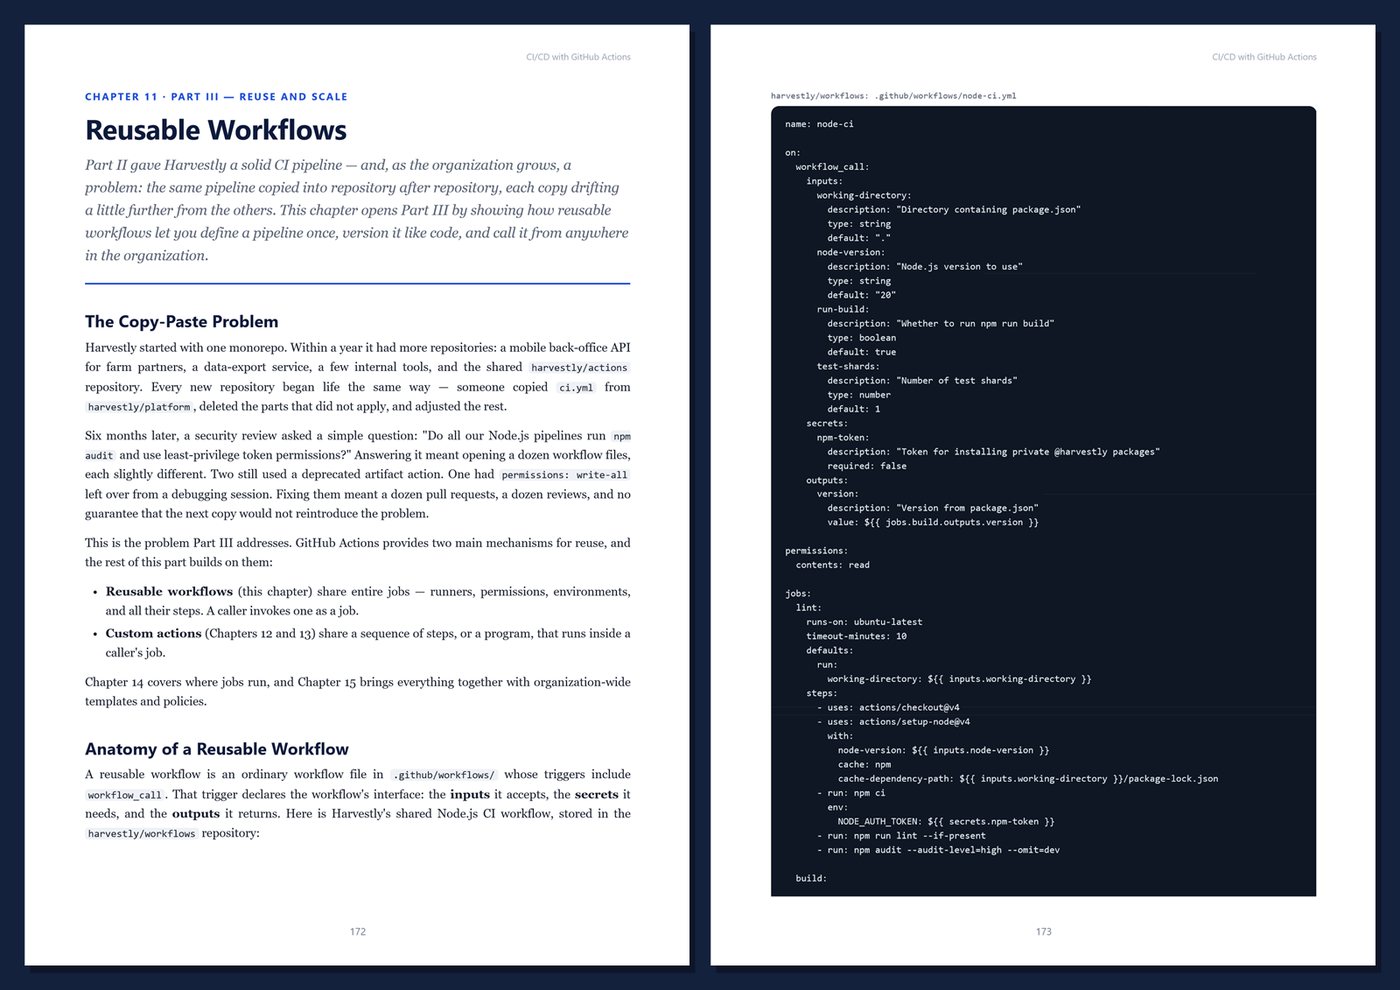
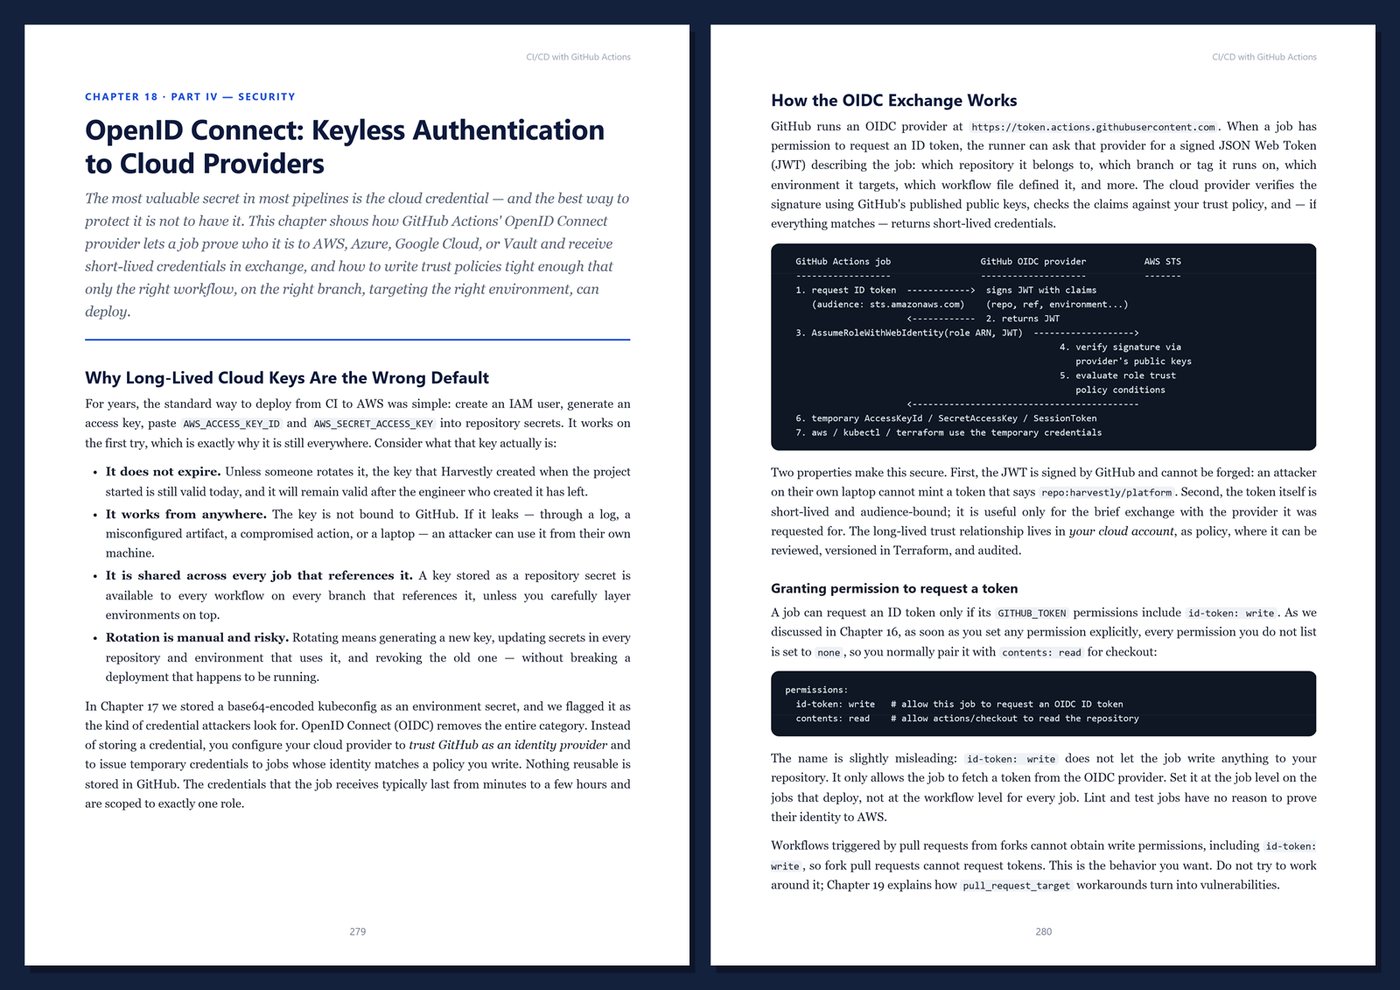
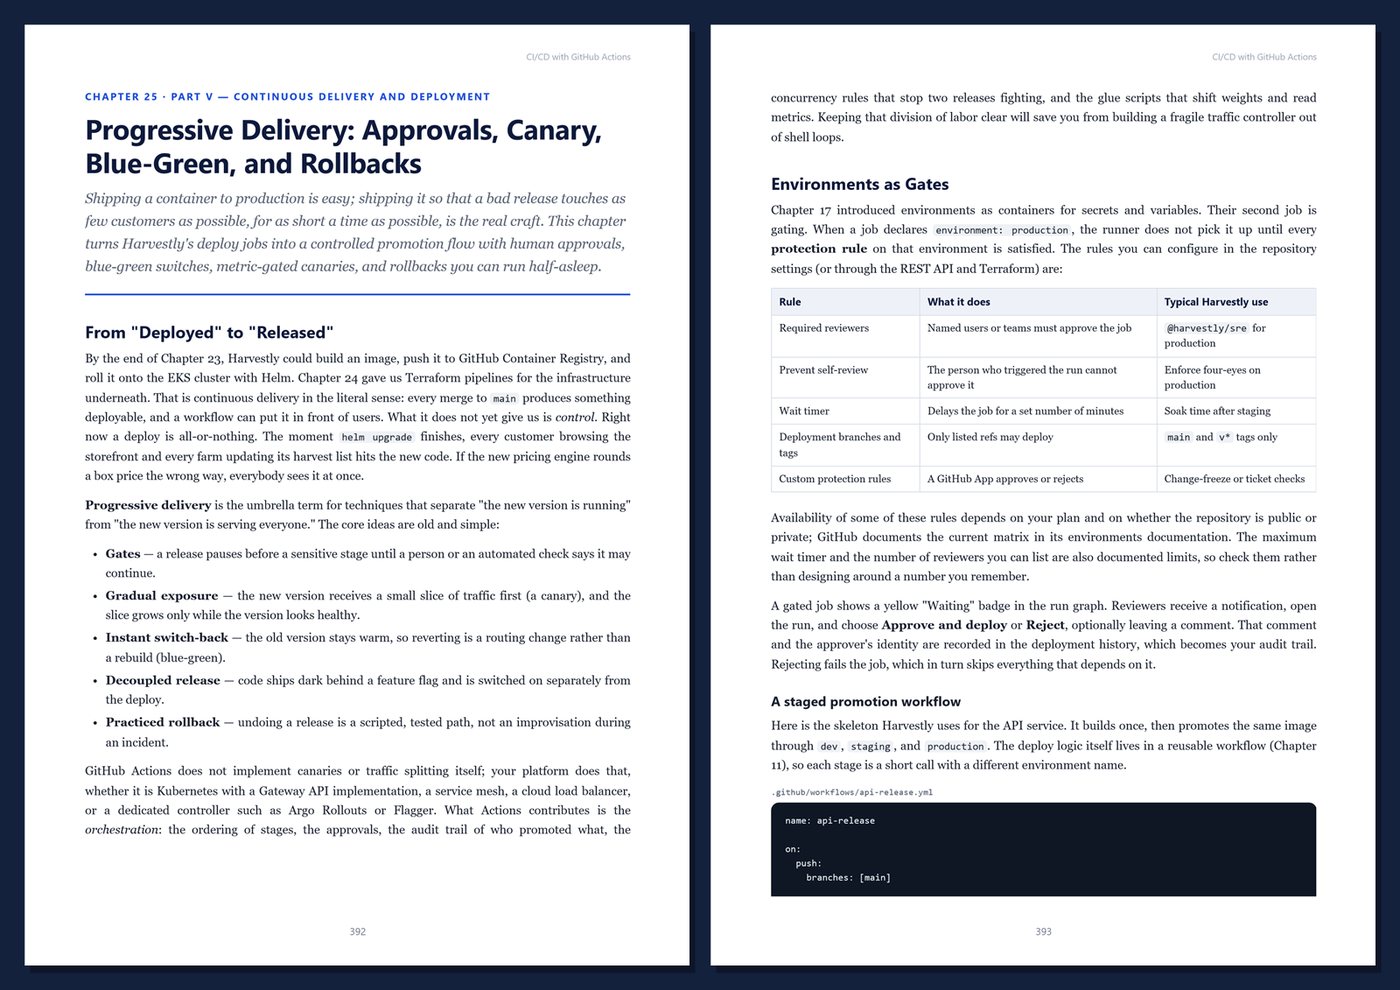
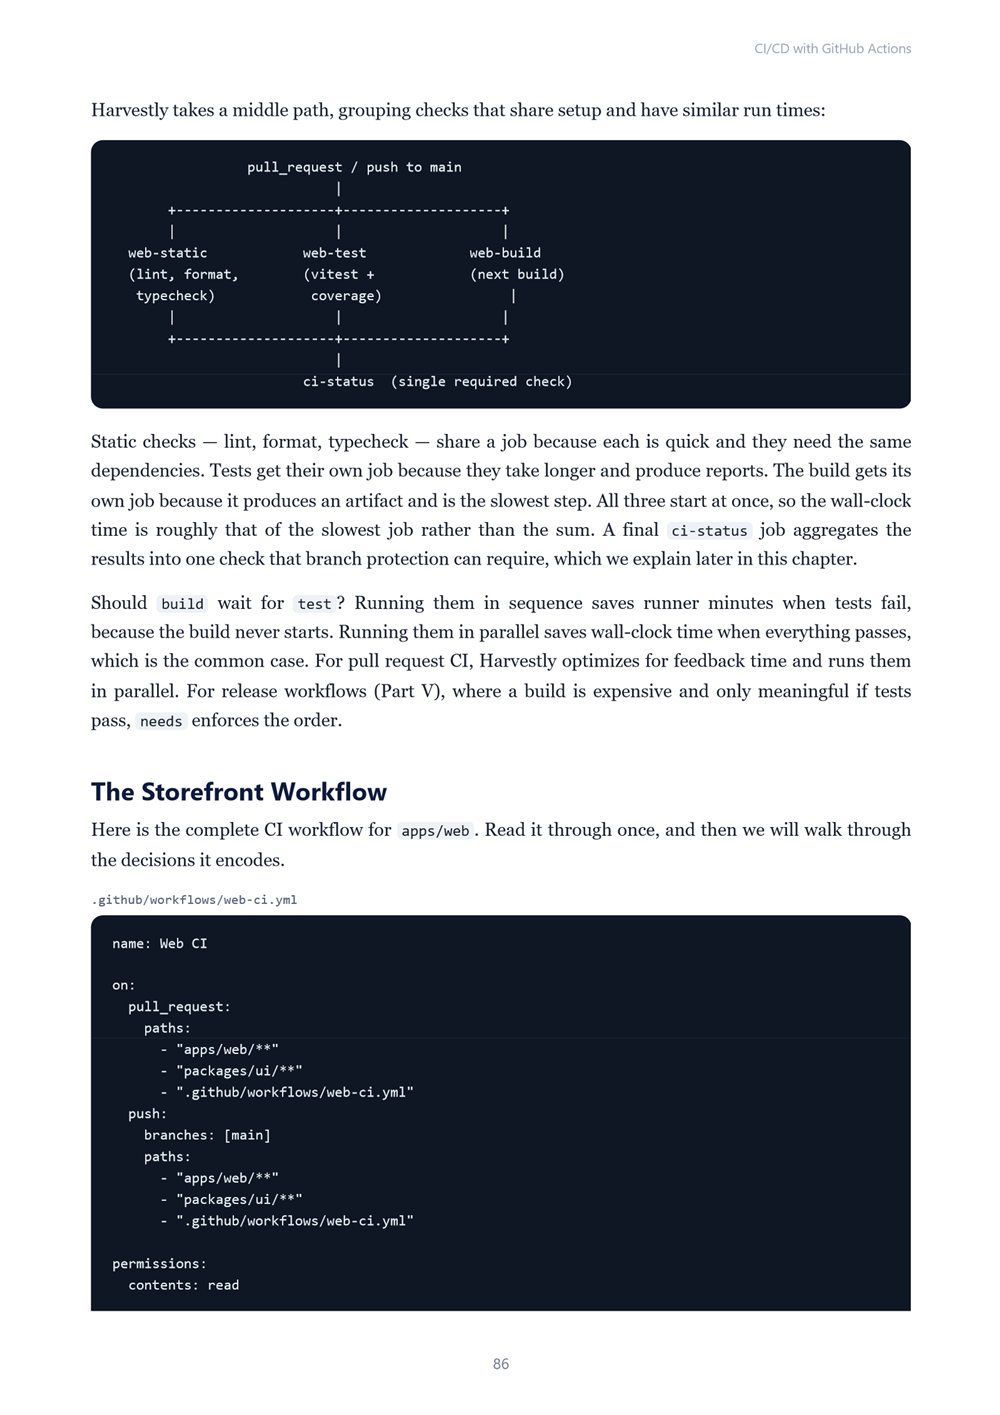
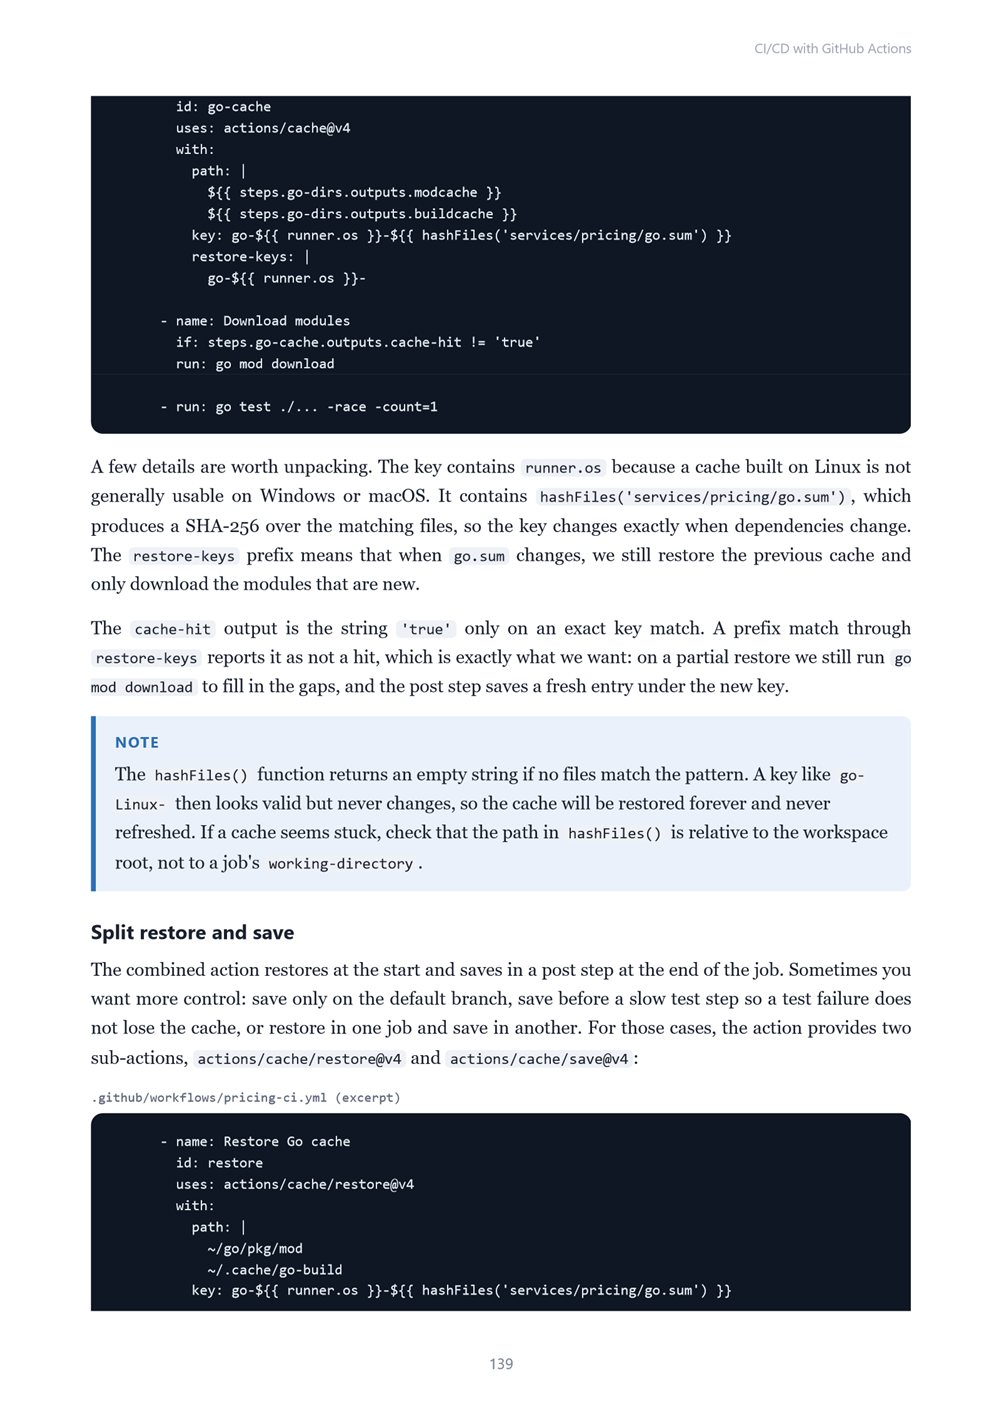
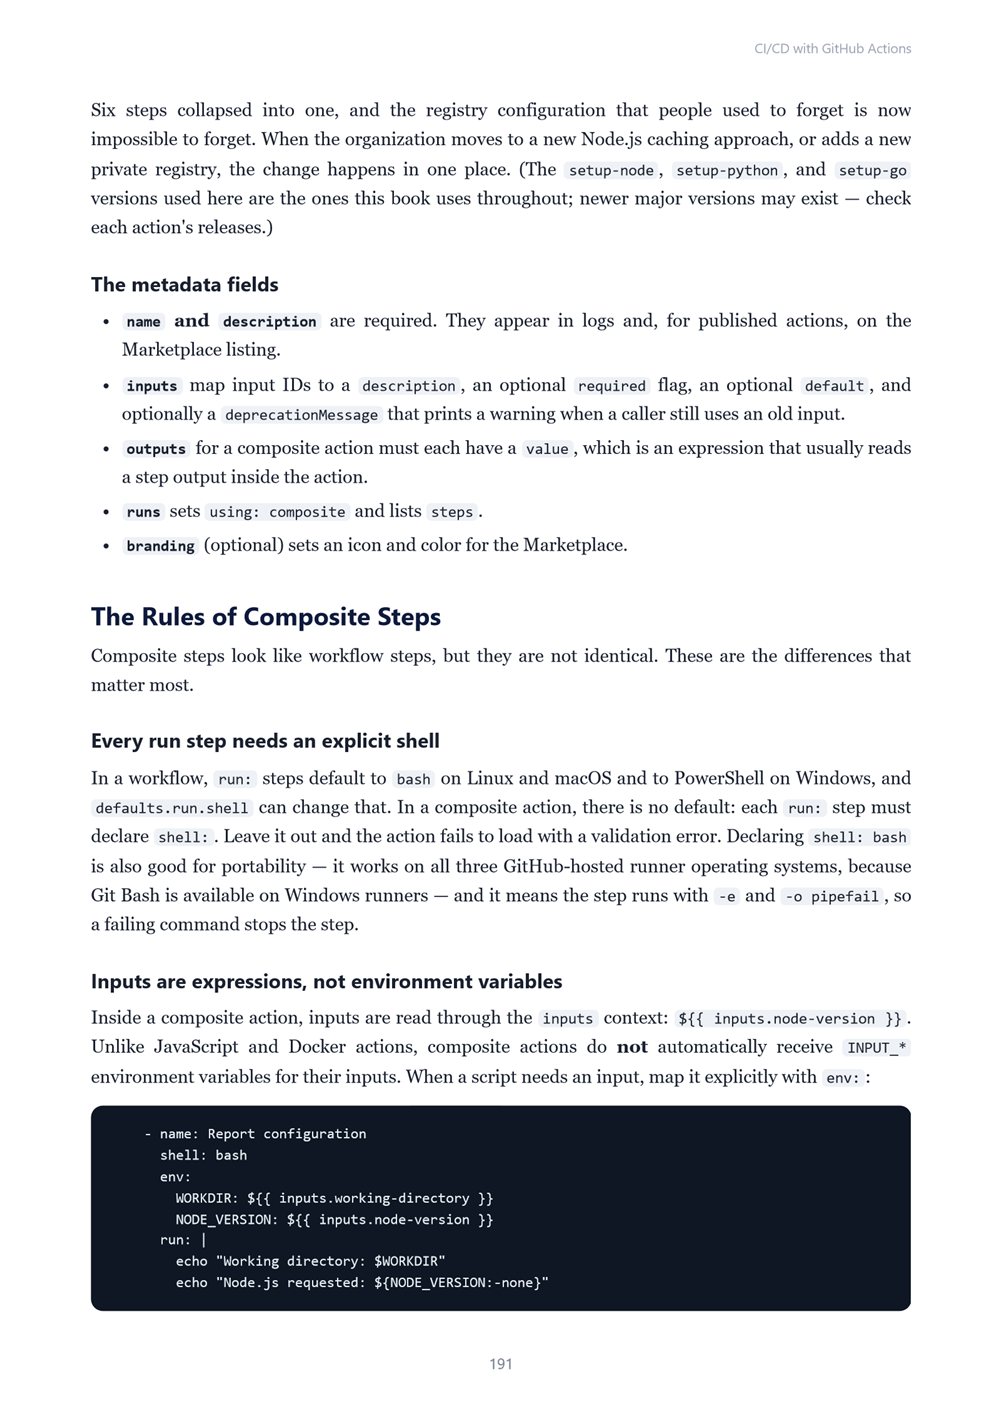
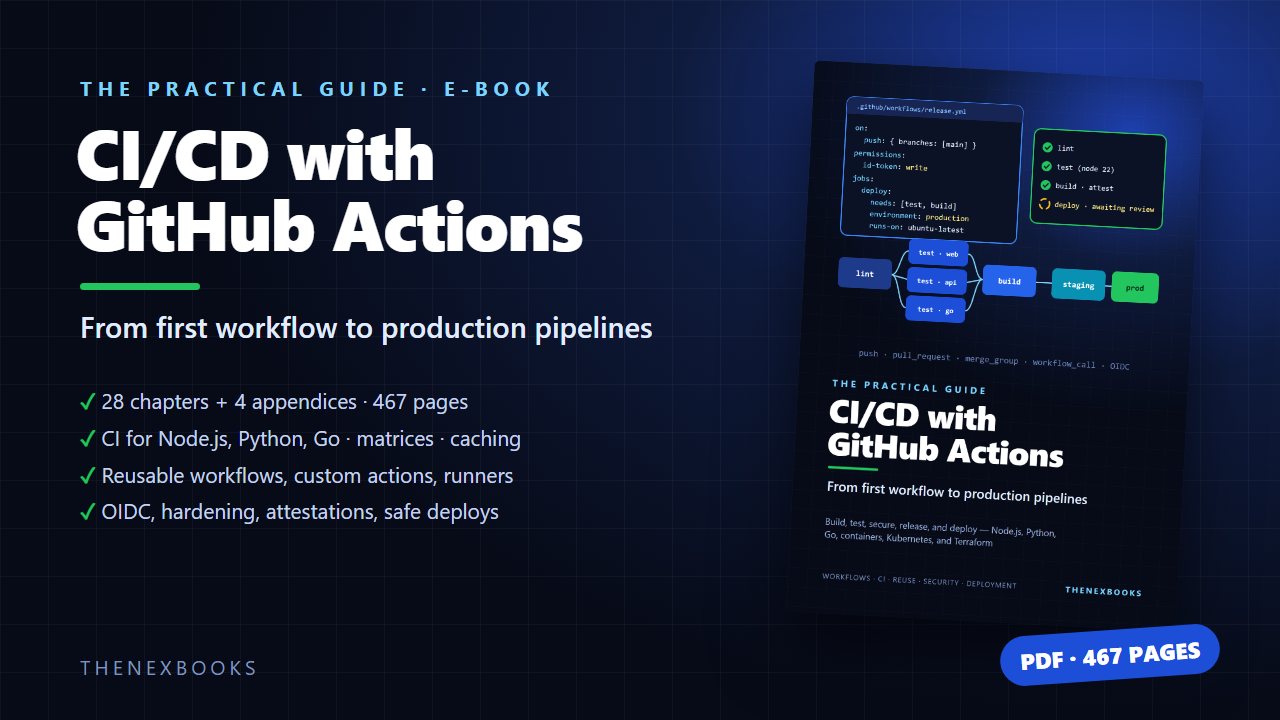
A 467-page practical guide to GitHub Actions: from your first workflow to secure, fast, reusable production pipelines that build, test, release, and deploy with confidence.
From First Workflow to Production Pipelines
Read before you buy: the PDF here is a free sample — the first 20 pages of the 467-page book (payments, sales and reviews on this demo site are sample data). Get the full e-book at thenexbooks on Gumroad.
Your first GitHub Actions workflow takes five minutes. A production pipeline your whole team trusts takes engineering.
Getting a green check on a pull request is easy. The hard part comes next: pipelines that stay fast as the codebase grows, tests that don't flake, YAML that isn't copy-pasted across forty repositories, tokens and secrets that can't be stolen, cloud credentials that never leak, releases that happen automatically, and deployments that can roll back in one step when something goes wrong on a busy morning.
This book shows you how to build all of it, step by step, with one realistic running example: Harvestly, a farm-to-door grocery platform whose monorepo holds a TypeScript and Next.js storefront, a Python API, a Go pricing engine, a shared UI package, Terraform infrastructure, and Kubernetes deployments.
- 467 pages · 28 chapters + 4 appendices
- Workflows, events, jobs, steps, runners, expressions, contexts, and conditionals in depth
- Complete CI for Node.js, Python, and Go with matrices, service containers, caching, and artifacts
- Required checks, merge queues, and path filtering for monorepos
- Reusable workflows, composite actions, and your own JavaScript and container actions
- GitHub-hosted, larger, and self-hosted runners, including Actions Runner Controller on Kubernetes
- Least-privilege GITHUB_TOKEN, secrets and environments, and OpenID Connect to AWS, Azure, and Google Cloud
- Hardening against script injection and pull_request_target pitfalls, and pinning actions by SHA
- Dependabot, code scanning, SBOMs, and artifact attestations for supply-chain security
- Container images and packages, release automation, Kubernetes deployments, and Terraform pipelines
- Approvals, canary and blue-green releases, rollbacks, debugging, performance, and cost optimization
- A complete case study: Harvestly's pipeline from first commit to production
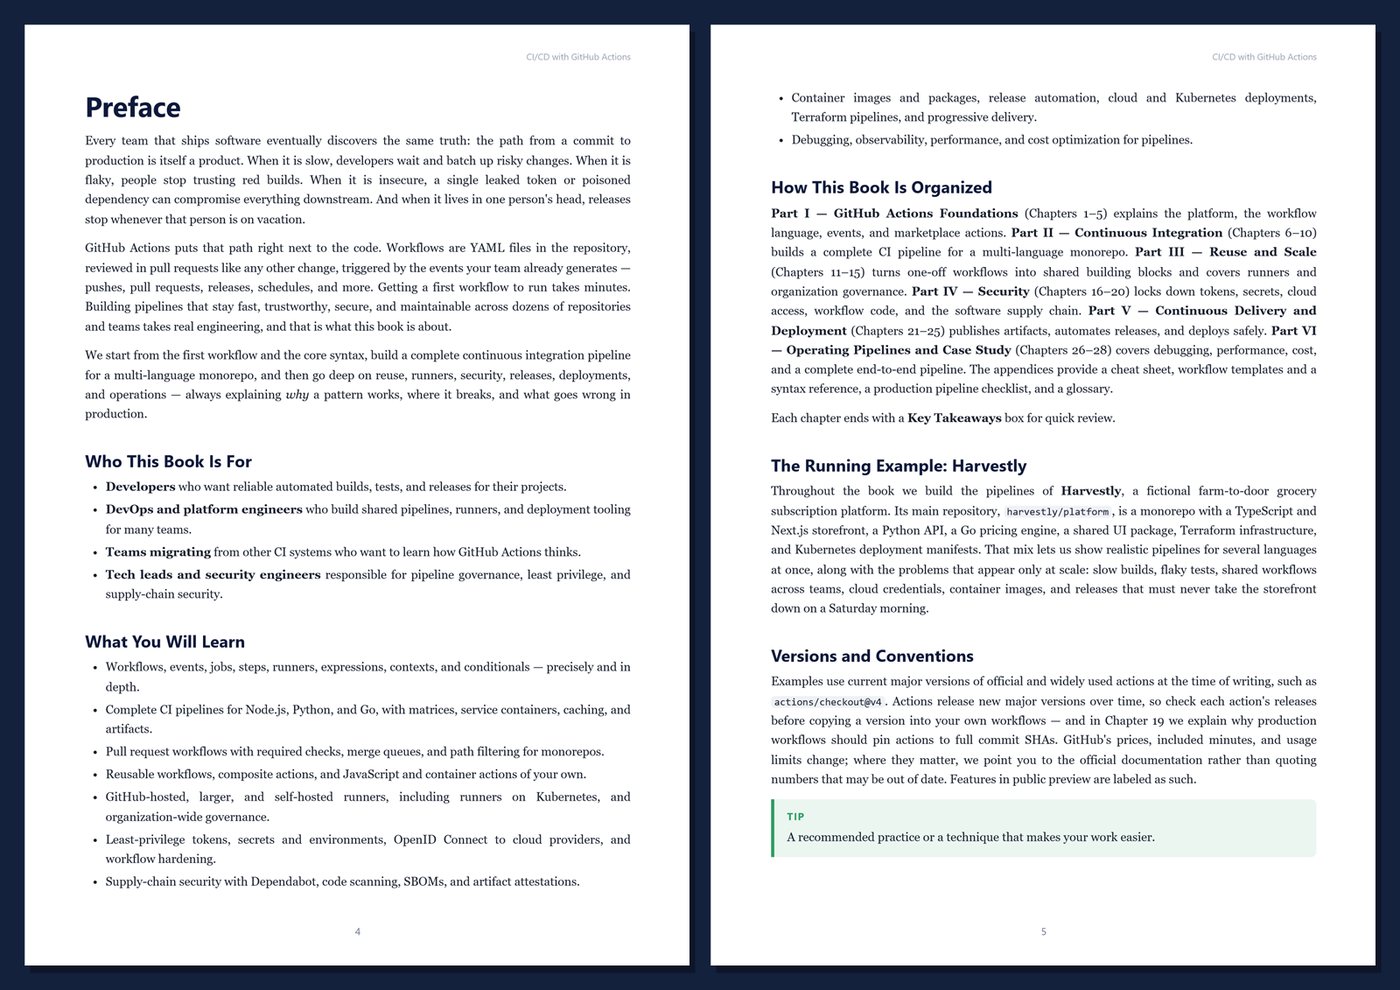
Table Of Contents
Part I — GitHub Actions Foundations
- Ch 1 · Why CI/CD, and Why GitHub Actions
- Ch 2 · Your First Workflow: Events, Jobs, Steps, and Runners
- Ch 3 · Workflow Syntax in Depth: Expressions, Contexts, Variables, and Conditionals
- Ch 4 · Events and Triggers: push, pull_request, schedule, workflow_dispatch, and More
- Ch 5 · Using Marketplace Actions: Versions, Inputs, Outputs, and Trust
Part II — Continuous Integration
- Ch 6 · Building a CI Pipeline: Lint, Test, and Build
- Ch 7 · Matrix Builds and Multi-Language Pipelines (Node.js, Python, Go)
- Ch 8 · Service Containers and Integration Testing
- Ch 9 · Caching, Artifacts, and Faster Pipelines
- Ch 10 · Pull Request Workflows: Required Checks, Merge Queues, and Monorepo Path Filtering
Part III — Reuse and Scale
- Ch 11 · Reusable Workflows
- Ch 12 · Writing Composite Actions
- Ch 13 · Writing JavaScript and Docker Container Actions
- Ch 14 · Runners: GitHub-Hosted, Larger, Self-Hosted, and Actions Runner Controller
- Ch 15 · Actions at Organization Scale: Templates, Policies, and Governance
Part IV — Security
- Ch 16 · GITHUB_TOKEN, Permissions, and Least Privilege
- Ch 17 · Secrets, Variables, and Environments
- Ch 18 · OpenID Connect: Keyless Authentication to Cloud Providers
- Ch 19 · Hardening Workflows: Script Injection, pull_request_target, and Pinning Actions
- Ch 20 · Supply Chain Security: Dependabot, Code Scanning, SBOMs, and Artifact Attestations
Part V — Continuous Delivery and Deployment
- Ch 21 · Building and Publishing Container Images and Packages
- Ch 22 · Release Automation: Versioning, Changelogs, and GitHub Releases
- Ch 23 · Deploying to Cloud Platforms and Kubernetes
- Ch 24 · Infrastructure as Code Pipelines with Terraform
- Ch 25 · Progressive Delivery: Approvals, Canary, Blue-Green, and Rollbacks
Part VI — Operating Pipelines and Case Study
- Ch 26 · Debugging, Troubleshooting, and Observability for Workflows
- Ch 27 · Pipeline Performance and Cost Optimization
- Ch 28 · Case Study: Harvestly's Pipeline from First Commit to Production
Appendices
- App A · GitHub Actions Cheat Sheet
- App B · Workflow Templates and Syntax Reference
- App C · Production Pipeline Checklist
- App D · Glossary
WHO IT IS FOR
Developers who want reliable automated builds, tests, and releases; DevOps and platform engineers building shared pipelines and runners for many teams; teams migrating from other CI systems; and tech leads and security engineers responsible for pipeline governance and supply-chain security.
FORMAT
PDF (A4), 467 pages, English, clickable table of contents and PDF bookmarks. 1st Edition, 2026. Published by thenexbooks.
This book is independent and is not affiliated with or endorsed by GitHub, Inc. or Microsoft. GitHub and GitHub Actions are trademarks of GitHub, Inc. All other product names are trademarks of their respective owners.
Book details
| Detail | |
|---|---|
| Pages | 467 |
| Format | PDF (A4) |
| Language | English |
| Level | Beginner to Advanced |
| Edition | 1st Edition, 2026 |
| Download on this site | Free sample, first 20 pages (PDF) |
| Publisher | thenexbooks |
Files you get
No reviews yet. Only buyers can review.
More from thenexbooks



